Every credential type is a trade-off between convenience, cost and how badly it fails when misused. There is no single right answer for a building — there is a right answer per door.
Cards and fobs
Cheap to issue, easy to revoke, universally understood. They are also trivially shareable and routinely lost. For a general office door with moderate turnover, that is an acceptable trade. For a server room, it is not, because a card proves only that the card was present.
PIN codes
No hardware to issue, which makes them useful for contractors and temporary access. But codes get written down, shared and rarely rotated. PINs work best as a second factor rather than a primary credential.
Biometrics
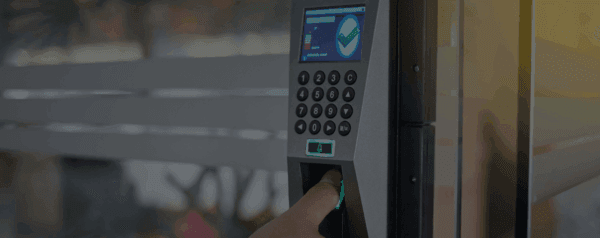
Fingerprint and facial recognition solve the sharing problem: the credential cannot be handed to someone else. They cost more per door, need thought about enrolment and privacy, and can struggle in specific conditions — gloved hands on an industrial site, direct sunlight on an outdoor reader. Used on the doors that matter, they are the strongest option available.
A practical pattern
- Perimeter and general office doors: cards, with a central directory for fast revocation
- Server rooms, cash handling, pharmacy and records: biometric, or card plus PIN
- Contractor and visitor access: time-limited PIN or temporary card, expiring automatically
- Anywhere attendance also matters: biometric, so the record reflects the person
Choose the credential by asking what happens if it is shared — not by asking which is newest.
The part that actually determines success
Whatever you choose, the system is only as good as the process behind it. Access must be revoked the day someone leaves, not the month after. Groups should map to roles rather than individuals. And someone needs to review the access list periodically. A biometric reader on a door whose permission list has not been audited in two years is still an open door.
Related services